Security
For the most confidential matters
JurisOne protects client data with controls the platform enforces itself, and a Named Authorised Individual’s sign-off before anything leaves the firm.
Explore the trust centreProtection built for legal work
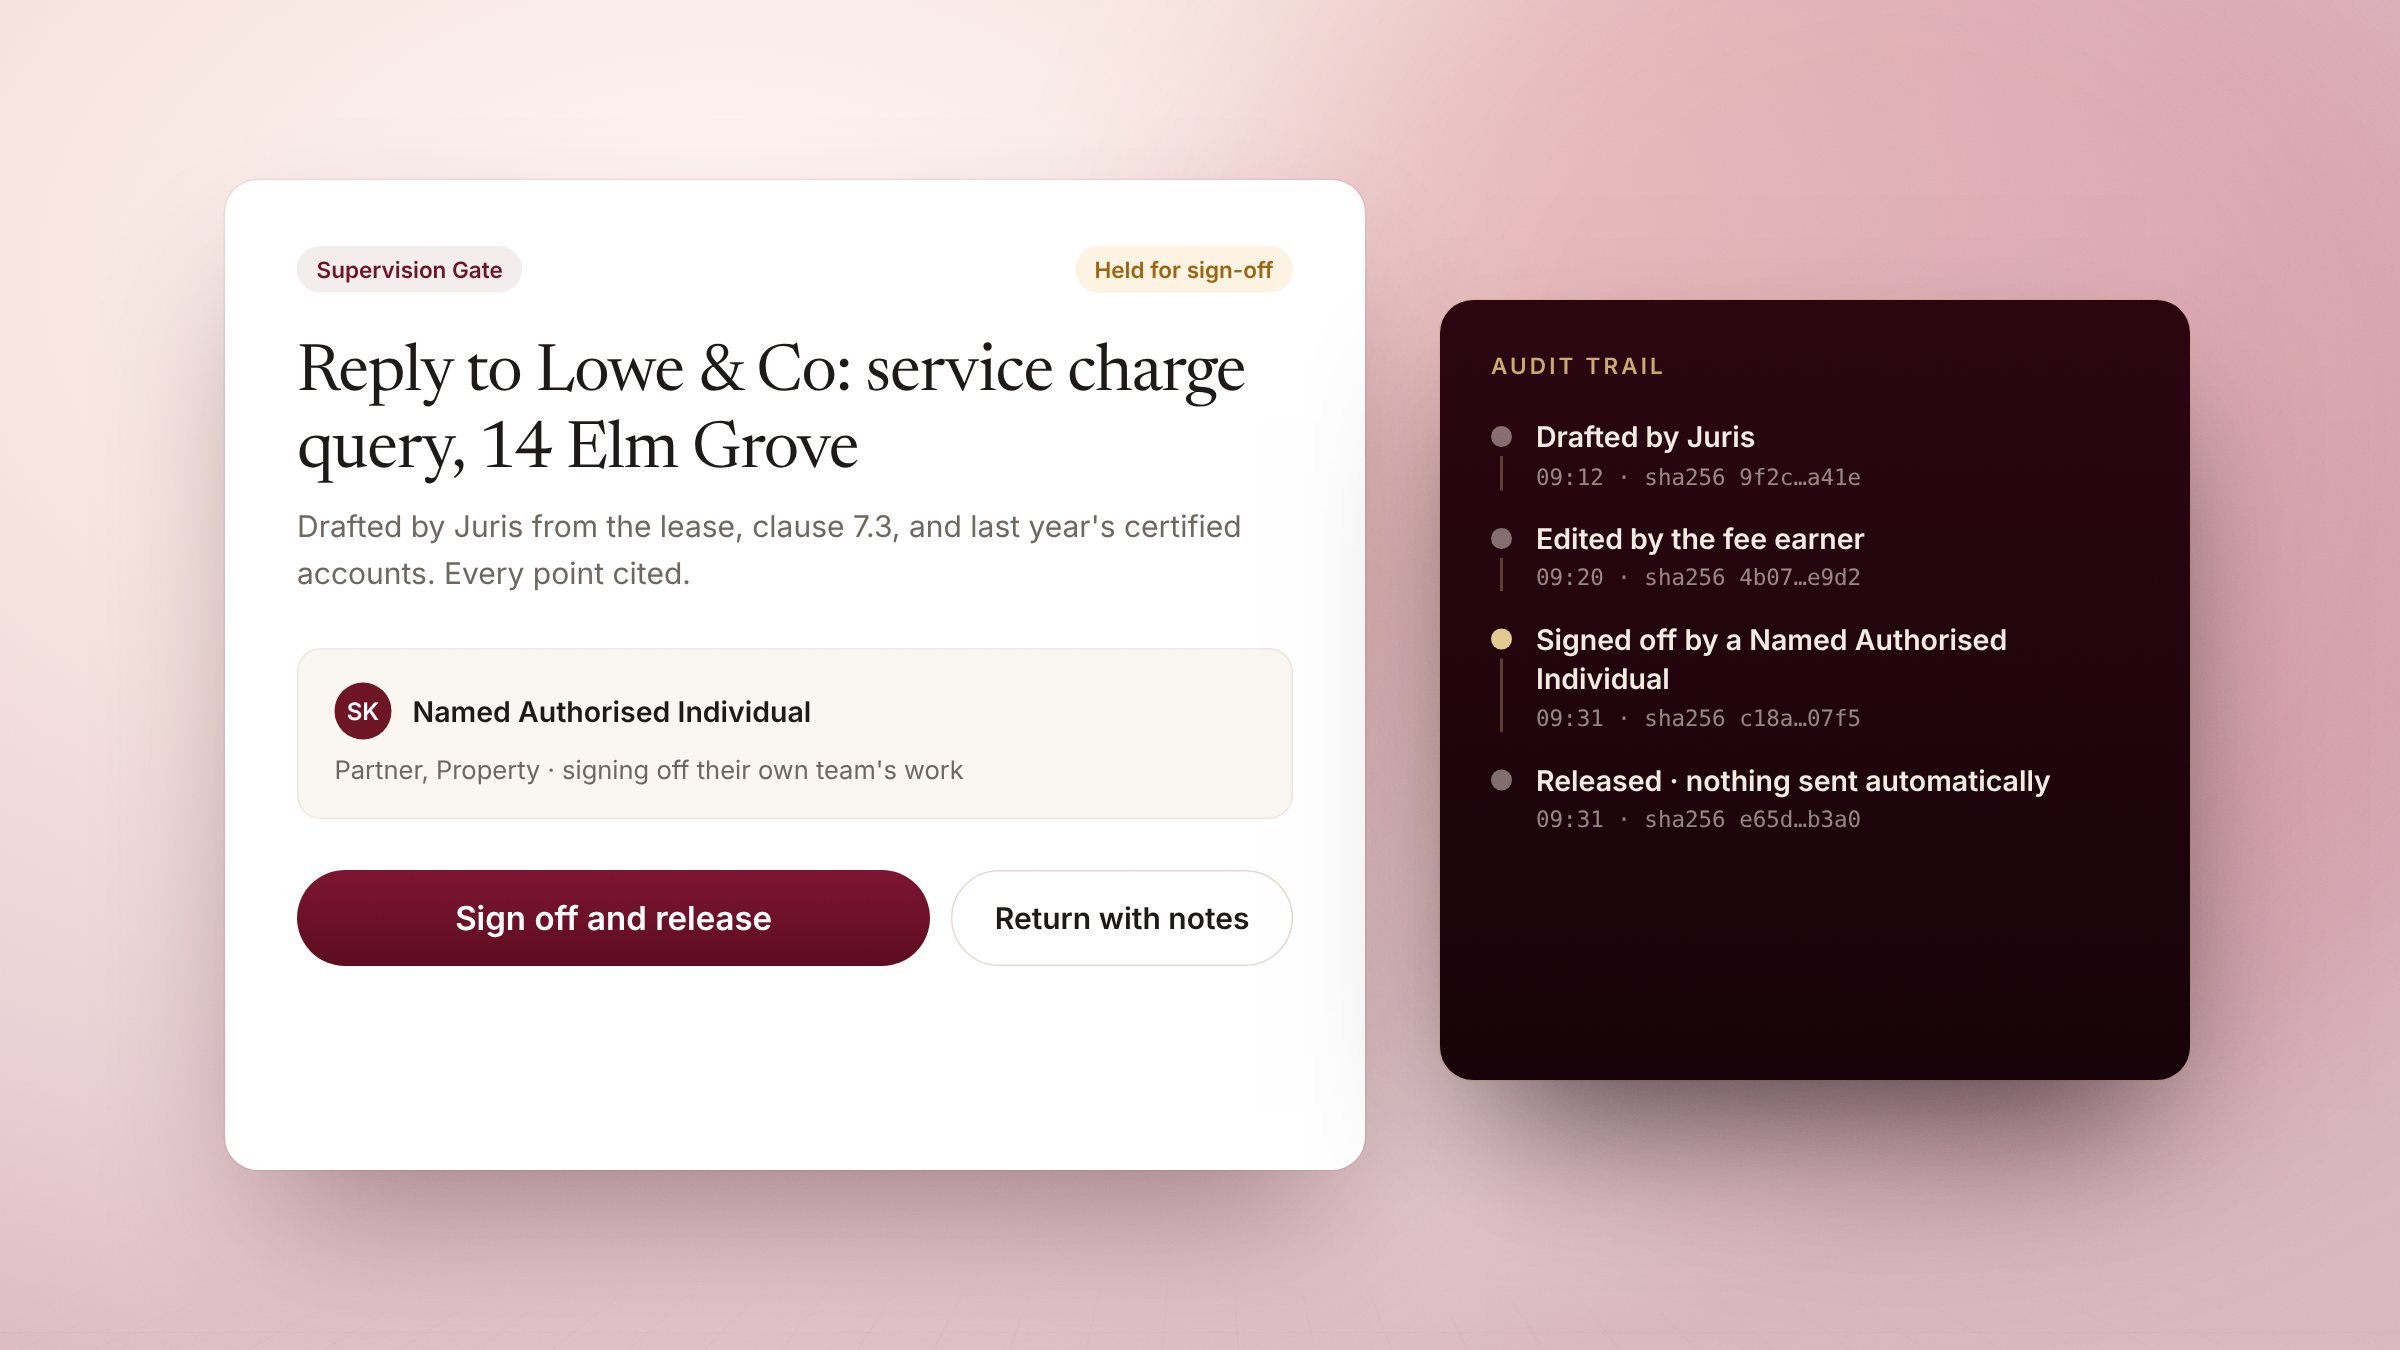
Sign-off before anything leaves
Every client-facing output waits at the Supervision Gate for a Named Authorised Individual. No setting turns it off, and every approval is recorded by name.
Client data never trains a model
Client data is never used to train models, by us or by the enterprise model providers we use. JurisOne does not train models on your matters.
Your firm controls its data
Your firm decides what to upload, how long to keep it and when to delete it. Retention is set by the firm, and records export per matter.
Ethical walls on every request
Walls and roles are checked in the database on every request, not only in the interface, so a walled matter stays invisible everywhere in the platform.
Roles that match how firms work
Partners, associates, paralegals and guests see only what their role allows, on the matters they are added to. Guests are read only, one matter at a time.
A record that shows any change
Every action and approval is written to a hash-chained audit trail that shows if anything has been altered, ready to export for clients, insurers and regulators.
Certifications and controls
We publish what we hold and what we are working towards, so your due diligence is straightforward. Further certifications are shown only once they are independently verified.
Explore the trust centreSecurity is part of everything we build
Supervision, access and audit aren’t features we added to an AI product. They are the product. Every matter is isolated to its firm, every request is checked against walls and roles, and every output is held until a Named Authorised Individual releases it. When something changes, the trust centre says so.
Explore the trust centreWhat does JurisOne treat as client data?
Everything your firm puts into JurisOne or Juris produces from it: matter documents, emails you file, prompts, drafts, outputs and the audit trail. It all belongs to your firm.
Is our client data used to train AI models?
No. Client data is processed through enterprise model APIs that do not train on it, and JurisOne does not train models on your matters.
Where is our data stored and processed?
With the hosting, storage and model providers named in our sub-processor list, with the regions each one uses. Request the list from the trust centre.
How do you respect ethical walls?
Walls and roles are enforced in the database on every request, so a blocked user cannot see a walled matter anywhere in the platform.
Can anything reach a client without review?
No. Every client-facing output waits at the Supervision Gate for a Named Authorised Individual, and the approval is recorded.
What certifications do you hold?
Cyber Essentials certified, October 2026. Further certifications, including SOC 2, are on our roadmap; we show them only once they are independently verified.
Can we get your security documentation for our due diligence?
Yes. Request our security pack from the trust centre and we will send policies, sub-processors and our answers to standard questionnaires.